
lea · Start
lea
Many Claude Code agents. None of your machine.
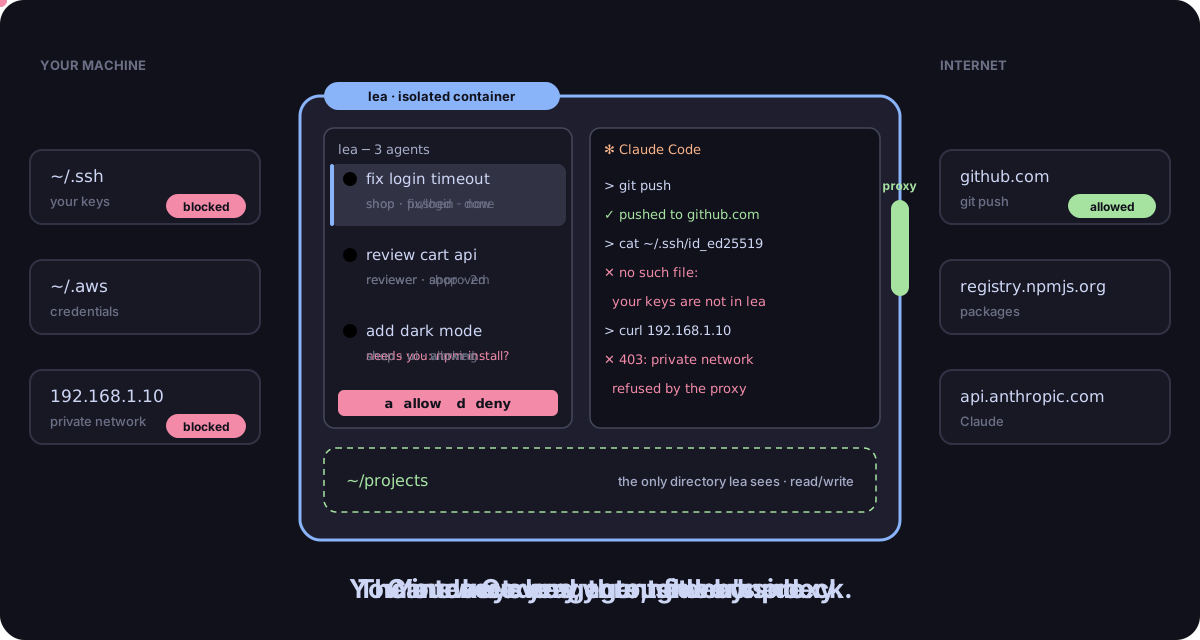
lea starts Claude Code in a container that sees one directory of your projects (read/write), a
read-only allow-list of your ~/.claude configuration (its own copy of your settings and
plugins, never written back), and nothing else of your machine. The
agents get their own container engine (so make test and docker run work), reach the
internet only through an egress proxy that refuses your private network, and never see your SSH
keys or credentials.
You drive them from the deck: a terminal with your agents in a column on the left and the selected agent's terminal on the right.
╭─ ●●● lea ──────── 3 agents ─╮│
│› ⠹ fix login timeout  42%   ││  ✻ Claude Code
│    shop · fix/login · 2m    ││
│  ● review cart api    18%   ││  > the timeout is set in session.go…
│    reviewer · shop · now    ││
│  ● add dark mode       7%   ││
│    shop · needs you         ││
╰─ n new · m msg · ? keys ────╯│
Why lea #
Claude Code does more when you stop approving every command, and a few agents in parallel do more than one. Both are risky on your workstation: an agent runs as you, with your keys, your tokens and your network. lea moves the boundary from the prompt to the container.
- Isolated by construction. What an agent can reach is fixed by the container and the proxy,
not by its good behaviour. A prompt-injected agent with every permission granted still cannot
read
~/.sshor call your intranet. - Many agents, one deck. States, context use, branches and each agent's own task report at a glance; one key to reach the next agent that needs you.
- Your Claude Code, unchanged. Your settings, permission rules, skills, plugins, hooks and
agents.
/plugin installworks inside lea, on lea's own copy: nothing reaches your host. lea runs the real Claude Code with your subscription or API key. - Local and open. No account, no server, no forge lock-in. Apache 2.0.
flowchart LR
  subgraph host["Your machine"]
    keys["~/.ssh, ~/.aws, ~/.kube<br/>Docker socket"]
    lan["Private network<br/>192.168.0.0/16, 10.0.0.0/8 …"]
    proj["~/projects"]
    cfg["~/.claude (allow-list)"]
    subgraph lea["lea container"]
      a1["agent: lead"]
      a2["agent: dev"]
      a3["agent: reviewer"]
      podman["rootless Podman"]
    end
    proxy["egress proxy"]
  end
  net["Internet: GitHub, npm, Claude API …"]
  proj <-->|read/write| lea
  cfg -->|read-only| lea
  lea --> proxy -->|HTTPS, pinned SSH| net
  proxy -.-x|refused| lan
  keys -.-x|not mounted| lea
Contents: Quick start · The deck · Git and forges · Databases · Queues and files · Logs · Web requests · Teams of agents · Commands · Configure · Safety · FAQ · Troubleshooting · Development